
The Security Risk Your CRM Strategy May Be Overlooking
For years, securing a CRM meant locking down logins, managing permissions, and keeping software patched. But CRM AI security risk is now a growing concern that businesses can no longer ignore.
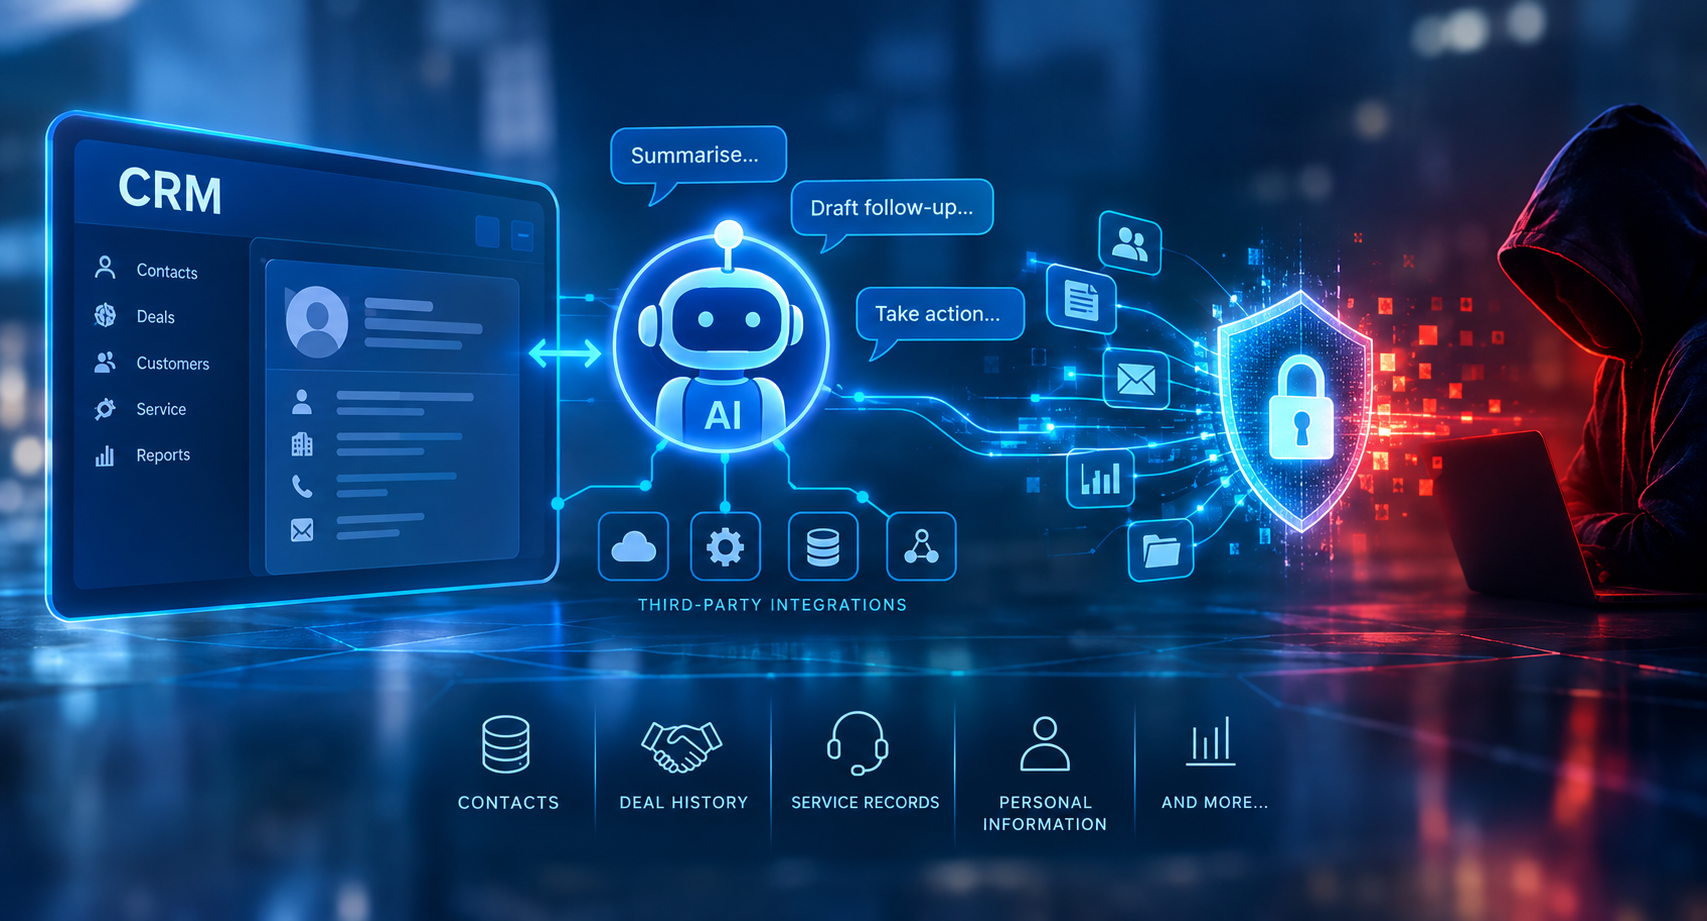
AI agents and chatbots are now plugged directly into CRM platforms, summarising conversations, drafting follow-ups, and acting on customer data automatically.
In doing so, they’re quietly becoming one of the easiest ways into that same CRM. 2026 has already shown what happens when that connection is exploited.
However, knowing the risk exists is only half the challenge. Without the right controls in place, AI integrations can quietly become your CRM’s biggest vulnerability.
At IT Solutions Consultancy, we help businesses adopt AI-powered CRM tools securely and strategically.
Here’s what you need to know to protect your business and how to act on it.
1. A Breach That Didn't Touch the CRM Directly and Still Got In
Earlier this year, attackers compromised an AI chatbot integration connected to Salesforce. It used stolen authentication tokens to pull data from hundreds of corporate CRM instances, without ever needing a password for the CRM itself. The chatbot had been granted access to make the integration useful. That same access became the way in.
It’s a telling pattern: the CRM wasn’t the weak point. The AI tool sitting next to it was. And because most organisations don’t review third-party AI integrations with the same scrutiny they apply to core systems, the access often sits there, quietly, long after anyone remembers granting it.
2. Why AI Makes CRM a Bigger Target, Not Just a Smarter One
Understanding CRM AI security risk starts with understanding agentic AI. AI that doesn’t just suggest an action, it takes it.This is now a mainstream feature of CRM platforms, not an experiment. Industry analysts estimate that a large majority of organisations already use some form of AI inside their CRM. Forecasts suggest task-specific AI agents will be embedded in a significant share of enterprise applications by the end of the year.
That’s a genuine step forward for productivity. It’s also a change in what a CRM actually is. A system that used to store customer records now has software connected to it. That software can read those records and act on them. If it’s compromised, it hands an attacker a single point of access to everything the CRM holds – contact details, deal history, service records, and often far more personal information than businesses realise they’re sitting on.
Recent industry research backs this up starkly: a majority of organisations report having experienced a data leak linked to AI tool usage in the past year. Only a small minority of organisations have a formal security policy covering how AI tools are allowed to connect to core systems like a CRM.
3. CRM AI Security Risk: What This Means for Your Business
The CRM AI security risk is not limited to large enterprises – smaller and mid-sized businesses are often more exposed, as they’re less likely to have a formal process for reviewing what an AI integration can actually see and do before it’s switched on.
A few questions worth asking before connecting any AI tool to your CRM:
- What data can it actually reach? Many integrations default to broad access because it’s simpler to set up, not because the use case requires it.
- Who approved the connection, and when was it last reviewed? Integrations tend to get set up once and forgotten. Access doesn’t expire just because attention moves on.
- What happens if the AI tool itself is compromised, not your CRM? If the answer is “the attacker gets the same access the AI tool has,” that’s the exposure you’re carrying right now.
- Is there a way to see what an AI agent has done, after the fact? Visibility into agent actions, not just customer-facing outputs, is becoming a baseline expectation, not a nice-to-have.
4. The Balance: Adopting AI Without Adopting the Risk Blindly
None of this is an argument against AI in your CRM as the productivity gains are real. The direction of travel isn’t reversing. It’s an argument for treating AI integrations as part of your security perimeter, not a bolt-on convenience feature that sits outside it.
Scope access deliberately. Review what’s connected on a regular cadence. Ask vendors direct questions about how their AI features authenticate and what they can see. Do this before it’s live, not after an incident forces the conversation.
If you’re already using AI features inside your CRM, or considering it, it’s worth having someone independently assess what access those tools actually hold. That’s often where the surprises are.
Conclusion: Securing Your CRM in an AI-First World
AI inside your CRM is no longer optional. It’s where the industry is heading. But with that progress comes a responsibility to treat AI integrations as part of your security perimeter, not an afterthought.
The businesses that will benefit most from AI-powered CRM are those that adopt it deliberately, with clear access controls, regular reviews, and full visibility into what their AI tools can see and do.
Contact IT Solutions Consultancy today to discuss how we can help you secure your CRM integrations and adopt AI confidently, without exposing your business to unnecessary risk.